Asos data breach: customer details accessed after hacker alert
Last updated on 12 October 2026
Asos says an attacker accessed customer names and contact details after getting into an employee account. Payment card details and passwords were not accessed.
Asos has confirmed that an unauthorised party accessed some customer personal information, including names and contact details, after gaining access to an employee account. It said payment card details and passwords were not accessed.
The retailer says no payment card information or account passwords were accessed, its website and app remained safe to use and customers do not need to take any action on their accounts.
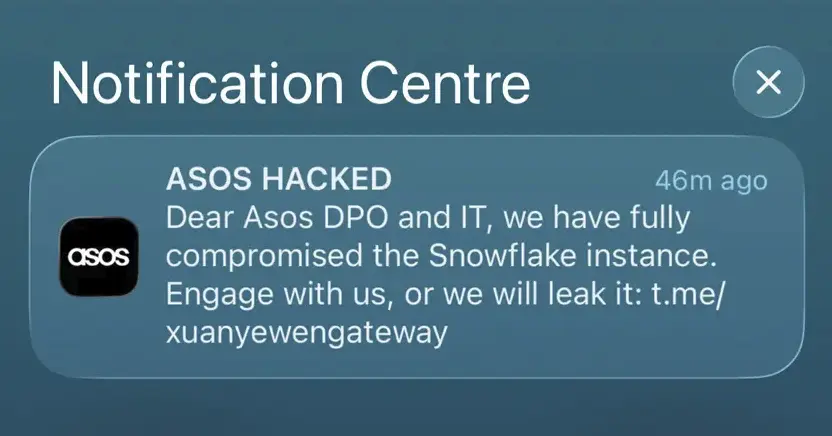
The update follows a mobile app alert titled “Asos hacked”, which was sent to customers on Tuesday 6 October and directed them to a Telegram account. In an email that evening, Asos apologised and told customers to ignore the notification and not click on the external link.
Nikki Stopford, co-founder of Consumer Voice, said:
“This gives customers a much clearer picture of what happened, and it’s reassuring that payment details and passwords weren’t accessed. But names and contact details did get into unauthorised hands, and that matters. They can be used to make scam emails, texts and calls look much more convincing.
“Asos now needs to tell affected customers directly exactly what information was accessed and whether there is anything else they need to do. In the meantime, people should be wary of unexpected messages claiming to be from Asos or offering refunds or compensation.”
Sign up to Consumer Voice for updates on data breaches that could affect you, plus practical advice on your rights, your money and ways to get back what you’re owed.
How the Asos data breach happened
Asos says an attacker gained access to an employee account by impersonating a trusted contact and obtaining their login details. Those credentials were then used to access information held on third-party platforms used by Asos.
The company says it immediately locked down the affected platforms to prevent further access and launched an investigation with internal and external cyber experts. It is also working with law enforcement and regulators.
The unauthorised notification sent on 6 October was addressed to Asos’s data protection officer and IT team rather than to customers. It claimed the hackers had compromised the retailer’s Snowflake data system and warned: “Engage with us, or we will leak it.”
Asos’s latest explanation does not say that Snowflake itself was compromised. Snowflake, a cloud company that stores data for many major businesses, has said it found no compromise of its platform.
What customer information was accessed?
Asos says the attacker had access to some personal information, including names and contact details, as well as what it describes as “certain non-personal account related information”.
It has confirmed that no payment card information or account passwords were accessed. It has not yet said how many customers had their personal information accessed or given more detail about the account-related information involved.
The retailer, which has 16.5 million active customers worldwide, says its website and app were safe to use throughout the incident and remain safe. It says there is currently no action customers need to take on their accounts.
The National Cyber Security Centre (NCSC) says Asos customers should assume they are affected, even if they did not receive the unauthorised notification. This is advice to take precautions, not confirmation that every customer’s data was accessed.
Asos says its full investigation will continue over the coming weeks and it will contact customers directly where it believes additional information, support or action is needed.
Watch out for scams following the Asos alert
Even though payment details and passwords were not accessed, names and contact details can still be used in scams. Criminals often exploit high-profile incidents like this, and suspicious messages may arrive some time after news of a breach.
Asos says there is no action you need to take on your account. But be cautious about unexpected emails, texts or calls claiming to be from Asos. The retailer says it will never ask you to provide passwords, security codes or payment details through an unsolicited message or call.
Be wary of emails, texts or calls claiming to be from Asos, your bank or a refund service, especially any offering refunds, compensation or help with your account. If someone calls unexpectedly about the incident, hang up and contact the organisation they claim to represent through its official channels.
There is no need to change your Asos password because of this incident based on what the company has found so far. As general good practice, however, use strong, separate passwords for your online accounts and turn on two-step verification where it is available.
Could Asos customers claim compensation?
The fact that customer information was accessed does not automatically mean people will be entitled to compensation.
You may be able to claim if an organisation failed to comply with data protection law and you suffered financial loss or distress as a result. You do not necessarily need to have lost money to make a claim.
It is still too early to know whether Asos customers could have a compensation claim. That will depend on what the continuing investigation establishes, including how the incident happened, which customers were affected and what impact it had on them.
Read our guide to data breach compensation to find out more about your rights.
Sign up to Consumer Voice for alerts on the latest data breaches, practical steps to protect yourself and updates on when you could be eligible for compensation.